Guest post by George Bailey, senior advisor, health IT/security, Purdue Healthcare Advisors.
The recent large-scale data security breaches experienced by major retailers Target Corp. and Neiman Marcus provide opportunities for learning across industries. These data breaches are painful for the companies, shareholders and, certainly, for the consumers victimized by subsequent fraudulent transactions on their financial accounts.
But once the dust settles, will these 110 million consumers suffer long-term damage to their privacy and financial security? I would argue no. Surprised? I say this because most of the attributes compromised in the Target and Neiman Marcus data breaches are short-lived items. By “short-lived,” I mean bits of information that can be changed or replaced by the consumer.
For instance, charge card numbers can be changed and accounts closed; debit card PINs can (and should) be changed; lost funds can be reimbursed; and credit scores reinstated. Now I don’t want to imply that this cleanup is easy, quick or inexpensive to do. It’s not. But looking three to five years into the future, these data breaches—just as the T.J. Maxx breach in 2007—will have little-to-no lasting effect on those compromised.
For the healthcare industry, a data breach is a quite different. A patient’s social security number (contained many times within healthcare records), medical history, psychiatric notes and sexual preference are not considered attributes that are “short-lived.” While a social security number can be changed, it’s a difficult and time-consuming process. The other data contained in a healthcare record is very sensitive, private, and cannot be re-written, as it is there to guide physicians in providing optimum care. Once sensitive electronic patient health information (ePHI) is lost, stolen or leaked to the Internet, it can spread faster than the best Facebook gossip and be cached, indexed and copied to a seemingly endless number of devices.
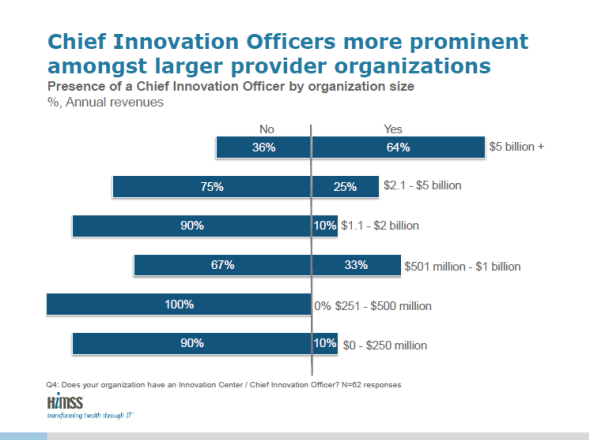
According to HIMSS, going beyond implementation of the electronic health record, healthcare providers increasingly look to innovation to reduce costs, improve patient care and increase patient safety. To learn more about how hospitals and health systems plan for, resource, and execute on their innovation agendas, HIMSS and AVIA launched the 2013 Healthcare Provider Innovation Survey. (Infographic below)
HIMSS and AVIA collaborated to produce the 2013 Healthcare Provider Innovation Survey, which was conducted by email from Aug. 20 to Sept. 30, 2013, with select U.S. hospitals, academic medical centers, children’s and ambulatory care centers to understand the current state of innovation within provider organizations. By analyzing the data collected from the 92 participants, HIMSS and AVIA determined the top barriers to innovation. The data is not necessarily meant to be representative of the market, but rather, facilitate dialogue about what the market is doing to determine the top barriers to innovation and other findings as reported in the results.
Eric Langshur, AVIA CEO, said: “The future of healthcare will be greatly influenced by providers’ ability to harness the latest technologies to positively impact their patients – and their bottom line.”
As most healthcare professionals know, an important step in the improvement of healthcare quality and cost will take place in October 2014, just under a year from now. This important step is the transition from ICD-9 to ICD-10 – with this new code set, the largest financial system change will take place since the Prospective Payment System (PPS) in 1983.
This change has to take place for several reasons including that with a maximum of 13,000 codes, ICD-9 is not specific enough for detailed diagnoses and the current codes do not reflect new services and technology in CMS payment systems. With more than 171,000 codes, ICD-10 will provide much more detailed clinical pictures and data, improving accuracy in all aspects of patient care. New data available through ICD-10 will help determine public health needs and identify trends, as well as helping to spot bioterrorism and epidemics.
The transition will not only impact healthcare organizations, but also physicians, for whom it will be particularly beneficial. Physicians will be able to determine the severity of illnesses more clearly, and, therefore, quantify the level of care more accurately. The codes will also create an electronic trail of documentation, which can help physicians receive proper payment and ensure their reputation remains in good standing.
With the importance and significance of this transition, it is crucial that ample preparations are made. However, there are many organizations that have not yet embarked on the road to preparedness and many concerns exist throughout the industry. For example, according to a survey conducted by the MGMA-ACPME of 1,200 office-based practices surveyed, approximately 70 percent of respondents were very concerned about expected loss of clinician productivity and the same percentage was very concerned about changes to clinical documentation. 71 percent surveyed responded that, in order to accommodate ICD-10, their EHR systems either were upgraded or still need to be upgraded, will need to be replaced, or they are unsure which. Only 0.6 percent had tested their EHRs for ICD-10 compliance.
Providence Hospital, located in downtown Columbia, South Carolina, is a 247-bed hospital founded in 1938 by the Sisters of Charity of Saint Augustine to minister to the community, in both body and spirit. The facility is best known for the expertise in cardiac care it provides through Providence Heart and Vascular Institute. With a hospital staff of more than 2,000 nurses, doctors and hospital administrators, Providence Hospital needed to standardize setup of user accounts and reduce the amount of time network engineers spent assigning rights in Active Directory.
Tony McNeil, technical manager said, “We have more demands on our department and we are not getting any additional staff because of the economic situation. Therefore, we have to work smarter and we need tools that help us work more efficiently.”
This became a perfect opportunity to put into action a permanent process for user account life cycle management utilizing Tools4ever’s complete User Management Resource Administrator solution.
Immediate delivery
Providence Hospital decided to implement UMRA to mainstream the provisioning process from the time an employee is hired and entered into the hospital developed, web based security application to the time they are entered into Active Directory. The previous process took nearly 2 days to complete before a user was ultimately provisioned in all systems. Now the process allows for an almost immediate creation of a user account with the correct provisioning. A web form allows for the assignment of group privileges and permissions to individual users. The application also creates the appropriate Exchange mailbox and creates a home folder for the employee on the appropriate share drive.
A bit of a “me too” post, but worth sharing nonetheless: Today, CCHIT announced a new strategic direction that will return it to its founding public mission of supporting the adoption of robust, interoperable health information technology. CCHIT plans to offer direct counsel to both healthcare providers and health IT developers on the requirements for certified EHR technology and how to best satisfy HIT regulations published by organizations and governments. With a more global focus, and in alliance with HIMSS, CCHIT will also develop new programs and policy guidance aimed at achieving interoperability and supporting change in the way providers and patients around the world use IT to positively transform health and healthcare.
“It’s apparent to both providers and vendors that the pace of ONC 2014 Edition certification has been slowed by the challenges of more rigorous criteria and testing, and the timing and nature of future federal health IT program requirements remain uncertain. With these changes, we canprovide a greater level of support and counsel to providers and vendors, something we could not undertake as a government authorized certification body,” said Alisa Ray, CCHIT executive director. “At the same time, returning to our independent work, we can convene thought leaders and advisory groups to provide policy and governance recommendations, and guidance to the healthcare community here and internationally.”
Carnegie Tri-County Municipal Hospital, a 21-bed facility in rural Oklahoma, was experiencing growing demand for wireless networking from their staff and patients. The hospital, which houses several clinics, offices and offers a variety of outpatient services, would benefit from a mobile Wi-Fi network improving staff productivity and patient experience. So leadership formulated a plan to upgrade its existing network with enhanced wireless access throughout the facility, as well as increase security and simplify management.
They approached Carnegie Telephone, the hospital’s telephone service provider, with the goal of obtaining a managed solution that met these requirements:
High-performance wireless network that could be segmented in to three mutually isolated networks – one for employees, one for patients and their families and the last for equipment like scanners, printers and other Wi-Fi enabled medical equipment
The network had to be easily and remotely manageable by Carnegie, ensuring quick deployment and trouble shooting for maximum uptime
Implementation on a limited budget for capital investment
Carnegie Telephone has been serving Oklahoma since 1903. It is been on the forefront of offering digital communications, HDTV and fiber broadband. To meet Carnegie Tri-County Municipal Hospital’s demands, Carnegie Telephone required a security appliance with features including content filtering, as well as Ethernet switches and high-performance wireless access points (APs).
In their product selection for the Carnegie Tri-County Municipal Hospital’s wireless network, Carnegie Telephone discovered a wireless APs. These APs had all the important enterprise features like multiple SSIDs and VLAN support to build multiple virtual wireless networks for the hospital. But the real kicker was a built-in controller that could be used to control up to 24 other Aps, from provider ZyXEL.
Security continues to be a major problem in health IT. The coming year will only bring more breaches and problems that must be addressed by those leading their organizations. In 2013 alone, millions of people were affected by breaches.
Breaches can be attributed to something as simple as a stolen device — flash drives and laptops, for example – to unauthorized access or disclosure of information by health system employees. For example, Healthcare IT News recently reported a four-year long breach by a single employee at the five-hospital Riverside Health System in southeast Virginia.
Health IT security issues are only going to get more pervasive, aggressive and encompassing in the years ahead. So, what can we expect as we look ahead? Here are some predictions about health IT security from the industry’s leading minds:
Remaining in compliance with these codes and regulations, like HIPAA, is key from a security point of view for healthcare organizations. Being compliant and ensuring that only the appropriate healthcare staff members and contract workers have access to the information they need to do their jobs ensures that the information remains secure and does not end up in the wrong hands.
Because of the sensitivity of the information accessed on a daily bases within a healthcare organizations and the number of people accessing the information – doctors, nurses, clinical and admin personnel, and contractors – IT security concerns will be slightly different than the highly publicized breaches we read about, like the recent Target breach that originated outside the organization.
QuantiaMD, the largest social learning network for physicians, developed by Quantia, Inc., conducted a recent poll of its members to understand physician perspectives regarding the implementation of the Affordable Care Act. Despite millions of enrollees, individuals and doctors remain confused about the law – a troubling fact as many patients look to their physicians as a primary resource on health care policy.
The poll garnered responses from 1,265 physicians from around the country and opened up a dialog about the ACA. Results of the study included:
84 percent of physicians said they did not feel like they had enough information on the ACA to serve as a reliable resource to their patients.
81 percent of physicians don’t feel they have enough information on the ACA to understand its impact on their practice and comply with its requirements.
When asked where they get the most reliable information about the ACA, the majority (35 percent) of physicians responded saying there aren’t any reliable sources of information.
79 percent said they would use an HHS-produced FAQ with their patients if such a resource were available.
“This poll proves how physicians have been left out of the health care reform process,” said Mike Paskavitz, Editor-in-Chief, Quantia, Inc. “As the patient’s most trusted point of access to the healthcare system, physicians can be a tremendous communication channel for the ACA, and this poll demonstrates that there hasn’t been much, if any, communication directed at them. This poll was a huge eye opener for Quantia and validates the importance of the Affordable Care Act curriculum we have been developing for our members.”